

Goode Exploits Vulnerable API and Admin Account to Carry Out Fraudulent Payments; Customer Card Information Leaked
Goode has explained that external attackers created fraudulent invoices in the company's Google Workspace (GWS) subscription payment feature and executed unauthorized payments using customer-registered cards. In a written response to a customer on October 30, Goode disclosed that attackers gained unauthorized access to the operation system through a "vulnerable API path" and subsequently exploited admin accounts.
According to Goode, the attackers fraudulently generated settlement and billing data for the GWS subscription service. Payments were executed through the existing auto-payment method, and the company stated that it cancelled all unauthorized payments on October 27. Goode explained that no external leakage of billing keys issued by the payment processor was confirmed.
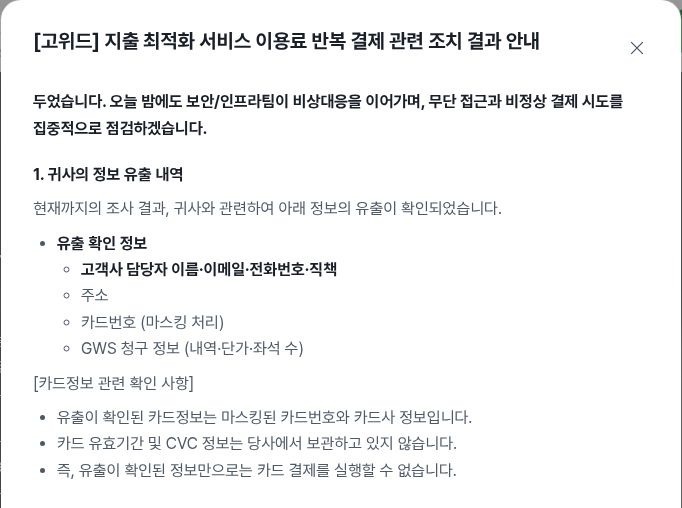
According to Goode's incident notification, customer contact information including names, email addresses, phone numbers, titles, and addresses of customer representatives, masked card numbers and card company information, and GWS billing information were leaked. In the October 30 written response, Goode stated that corporate cards other than affiliated cards were also included in the scope of the breach. However, Goode said it was unable to confirm the actual masking format of the customer's card that received the response.
The affected customer stated they had previously received a phone explanation that "card numbers were not leaked" and requested confirmation. Goode apologized for insufficient explanation distinguishing between full numbers and masked numbers, and clarified that the leaked information consisted of partially displayed numbers out of 16 digits.
Goode explained that in currently analyzed logs, all attempts to view full card numbers failed, and the company does not store card expiration dates or CVC. The company stated that on October 27, it blocked abnormal access IP addresses, vulnerable API paths, and related payment functions, and reported the security breach to the Korea Internet & Security Agency (KISA). Further investigations by external agencies are underway, and the company plans to finalize and announce a compensation plan by the end of November.
Loading comments…