
Hacking Crisis Sweeps Entire Financial Sector…Banks Followed by Insurance and Securities Companies Under 'Infiltration'
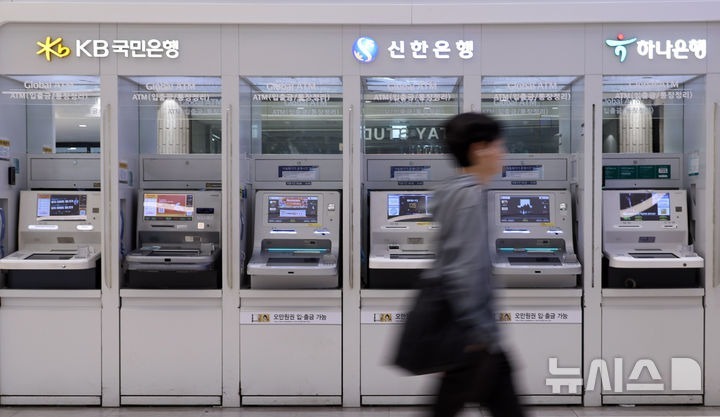
Sophisticated hacking attempts exploiting artificial intelligence (AI) are spreading across the entire financial sector, extending beyond commercial banks to secondary financial institutions and insurance and securities companies. This series of hacking incidents, spearheaded by advanced AI agents, is lighting red warning lights not only for private financial companies but also for central and local government computer networks handling vast administrative data.
Seven Financial Companies Hit Simultaneously…Same IP and AI Infiltration Tool Traces Detected
According to financial authorities and security industry sources on the 5th, recent breach incidents have occurred consecutively at a total of seven financial companies including commercial banks such as Shinhan, KB Kookmin, Hana, and Busan Bank, as well as secondary financial institutions including Yegaram and Welcome Savings Bank, and Hyundai Capital.
The decisive characteristic that distinguishes this incident from previous hacking is the speed and automation of the attack. According to investigations by authorities and security industry experts, identical circumstances were detected in which the same attackers attempted infiltration by changing countries and IPs against these financial companies. In particular, traces of AI-based penetration tools such as Chinese-based 'ARTEX AI (Autonomous Penetration Testing Console)' were discovered on some attack servers, prompting investigative authorities to examine the connection.
Unlike the past when humans manually searched for vulnerabilities, it has become evident that AI agents rapidly scanned system loopholes and indiscriminately penetrated them. Consequently, even the securities and insurance industries, where direct damage has not yet been confirmed, have begun emergency security inspections and entered emergency mode.
Authorities Convene Entire Financial Sector…"Security Paradigm Must Shift with AI Shield"
Financial authorities are treating the gravity of the situation seriously and have urgently convened the entire financial sector, ordering comprehensive re-inspections of externally exposed systems. Security experts agree that this incident should serve as an opportunity to move away from traditional reactive responses and network segmentation-focused security systems.
"Under the assessment that human defensive capabilities are insufficient to keep pace with the speed of AI-powered hacking," the financial sector overwhelmingly emphasizes that defense systems must likewise be comprehensively upgraded to AI-based real-time detection and blocking systems.
This AI hacking shock that has struck the financial sector is not limited to the private sector. Experts point out that computer systems of central government ministries and local governments handling sensitive personal information such as resident registration, welfare, and taxation, as well as critical national administrative data, are likewise exposed to similar intelligent threats.
In particular, local governments may have relatively weak information security budgets and specialized personnel, raising concerns that they could be left defenseless against AI-driven intelligent infiltration attempts. Experts point out that government ministries and local governments must likewise expedite precise diagnostics to determine whether there are any traces of infiltration across external connected systems and overall administrative support solutions.
The double-edged sword created by technological evolution has already emerged as a real threat. This is a golden time when not only private financial companies must strengthen their internal controls thoroughly, but also central and local governments must accelerate rigorous security inspections of their entire administrative computer networks.