

Editorial Personal Information Exposure of Air Force One: Opportunity for Comprehensive Security Review of National and Local Government
National Critical Information Leaks and Vulnerabilities in Management Systems
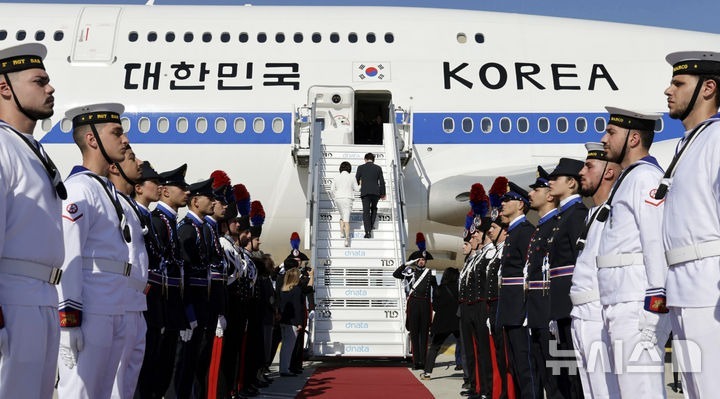
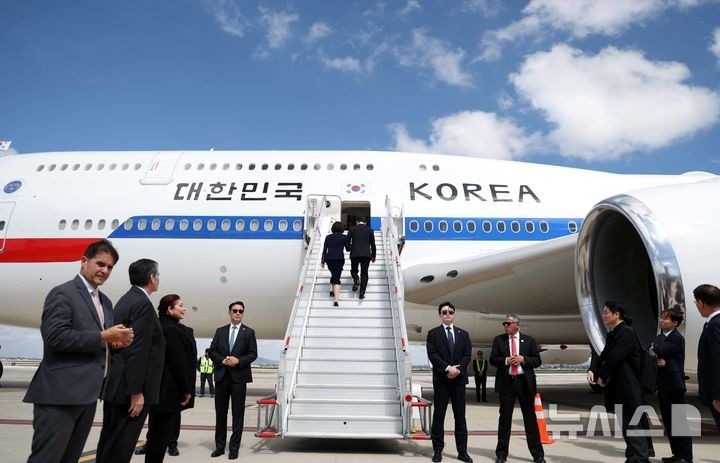
The incident in which personal information of 168 passengers aboard the presidential aircraft (Air Force One) was exposed on an external malware analysis website sounds a serious alarm on the public sector's information asset management practices. The exposed list included sensitive information that should have been protected, including dates of birth and passport numbers of President Lee Jae-myung and his spouse, National Security Office and Presidential Security Service officials, and accredited press corps members.
Information about a presidential overseas visit is core data that directly reveals the movement of the supreme commander-in-chief and the personnel composition of security lines. The fact that such information was exposed on an external paid platform indicates there were management lapses throughout the entire process of data creation, distribution, and disposal. Given that the government stated it had previously identified this and completed deletion measures, this must not remain a temporary fix but must lead to fundamental investigation of root causes and establishment of recurrence prevention measures.
Strengthening Technical Defense and Institutionalizing Data Handling Guidelines
First, there is a need to further strengthen information security management standards at the national level. Technical blocking systems (DLP) must be enhanced to prevent documents containing sensitive information from being introduced to unverified external sites or third-party platforms. Additionally, data handling procedures related to diplomacy and security must be detailed, and legislative work should proceed in parallel to mandate high-level encryption and de-identification processing from the document creation stage.
Necessity for Comprehensive Security Audits of Local Governments and Public Sector
This review must not be confined to the central government. Local governments and public institutions nationwide also handle personal information of numerous residents and public officials in the process of conducting overseas business trips, international exchanges, and large-scale events. To prevent similar incidents from occurring at the local government level, where relative security management capacity may be weaker, comprehensive security audits and preemptive measures must be established.
Security's essence is prevention before incidents occur rather than response after they happen. We hope that a real-time monitoring system will be established throughout the public sector, and that this incident will become an opportunity to elevate the nation's overall cyber security infrastructure to a higher level.
Loading comments…